Troubleshooting
Ivanti Policy Secure(IPS) provides logging and monitoring capabilities to help you track events and user activities. The system generates event logs related to system performance, administrator actions, network communications, access management framework results, user sessions, and so forth.
The available logs, includes:
- Event Logs- This file contains a variety of system events, such as session timeouts, systems errors and warnings, server restart notifications and connectivity requests.
- Admin Access Logs- This file contains administration information, including administrator changes to user, system and network settings, such as changes to session timeouts, license changes and so on.
TACACS+ Event and Admin Logs
Event Logs
- Logging when count of TACACS+ connection reached system limit.
Minor – Limit of <max count> TACACS+ concurrent users reached
Minor | TAC31628 | 2018-01-31 14:40:48 - ic - [127.0.0.1] System()[] - Limit of 2 TACACS+ concurrent users reached |
|---|
- Dropping the incoming TACACS+ connection because received from unknown host.
Major - TACACS+ request received from unknown TACACS+ client <switch IP>
Major | TAC31629 | 2018-01-31 14:37:54 - ic - [127.0.0.1] System()[] - TACACS+ request received from unknown client 10.204.89.239 |
|---|
- Dropping the incoming TACACS+ connection due to shared-secret mismatch.
Minor - Invalid TACACS+ packet from <switch IP>, discarding.
Minor | TAC31628 | 2018-01-31 14:35:58 - ic - [127.0.0.1] System()[] - Invalid TACACS+ packet from 10.204.89.239, discarding. Incorrect shared secret |
|---|
Admin Access Logs
- Exec Authorization [Only when Authorization is enabled under authorization setting]
- Log for exec authorization success
TACACS+ Shell authorization successful for <user> on switch-<switch ip> and attributes are: privilege = %d, idle-timeout = %d, session-timeout = %d
Info | TAC31611 | 2018-01-30 18:59:03 - ic - [xx.xxx.xx.xxx] tac_user(tac_admin_realm)[tac_admin_role] - 'TACACS+ Shell authorization successful for tac_user on 10.204.89.239 and attributes are: privilege = 15, idle-timeout = 5, session-timeout = 60' |
|---|
- Log for exec authorization failure due to no shell policy assigned to roles.
TACACS+ Shell authorization rejected for <user> on switch-<switch ip>. Reason- %s
Reasons-
- No session found
- No Shell policy found for the assigned roles
Info | TAC31612 | 2018-01-30 19:06:45 - ic - [xx.xxx.xx.xxx] tac_user(tac_admin_realm)[tac_admin_role] - 'TACACS+ Shell authorization rejected for tac_user on 10.204.89.239. Reason: No Shell policy found for the assigned roles' |
|---|
- Command authorization [Only when Authorization is enabled under authorization setting]
- Log for command authorization success.
TACACS+ Authorization successful for command-%s from <user> on switch-<switch ip>
Info | TAC31611 | 2018-01-30 19:08:14 - ic - [xx.xxx.xx.xxx] tac_user(tac_admin_realm)[tac_admin_role] - 'TACACS+ Authorization successful for command-'show version' from tac_user on 10.204.89.239' |
|---|
- Log for command authorization failure due to no shell policy assigned to roles or due to deny under command set.
TACACS+ authorization rejected for command-<cmd> from <user> on switch-<switch ip>. Reason- %s
Reasons-
- No session found
- No Shell policy found for the assigned roles
Info | TAC31612 | 2018-01-30 19:37:02 - ic - [xx.xxx.xx.xxx] tac_user(tac_admin_realm)[tac_admin_role] - 'TACACS+ authorization rejected for command-'show version' from tac_user on 10.204.89.239. Reason- No session found' |
|---|
- Matched with the rule – [command = %s, Arguments = %s, action = %s] in shell policy-%s
Info | TAC31612 | 2018-01-30 19🕚31 - ic - [xx.xxx.xx.xxx] tac_user(tac_admin_realm)[tac_admin_role] - 'TACACS+ authorization rejected for command-'menu ' from tac_user on 10.204.89.239. Reason- Matched with the rule – [command = menu, Arguments = null, action = deny] in shell policy-tacacs_policy' |
|---|
- No match found. Default action is deny in shell policy-%s
Info | TAC31612 | 2018-01-30 19🕛31 - ic - [xx.xxx.xx.xxx] tac_user(tac_admin_realm)[tac_admin_role] - 'TACACS+ authorization rejected for command-'display arp' from tac_user on 10.204.89.239. Reason- No match found. Default action is 'deny' in shell policy-tacacs_policy' |
|---|
- Login Authentication: [Only when Administrator login is enabled under admin access setting]
- Login Success
Info | AUT30684 | 2018-01-30 18:59:02 - ic - [ xx.xxx.xx.xxx ] tac_user(tac_admin_realm)[] - Primary authentication successful for tac_user/System Local from 10.204.59.223(Shell login to 10.204.89.239). |
|---|
- Login failure due to authentication failure.
| AUT23458 | 2018-01-30 19:15:10 - ic - [10.204.59.223] tac_user(tac_admin_realm)[tac_admin_role] - Login failed using auth server System Local (Local Authentication). Reason: Failed |
|---|
- Login failure due to restrictions.
Info | AUT23458 | 2018-01-30 19:04:23 - ic - [xx.xxx.xx.xxx] tac_user(tac_admin_realm)[tac_admin_role] - Login failed. Reason: No Roles |
|---|
- Login failure due to no role available.
Info | AUT23458 | 2018-01-30 19:04:23 - ic - [xx.xxx.xx.xxx] tac_user(tac_admin_realm)[tac_admin_role] - Login failed. Reason: No Roles |
|---|
- Session deletion due to accounting stop received
Info | AUT31627 | 2018-01-30 19:23:43 - ic - [xx.xxx.xx.xxx] tac_user(tac_admin_realm)[tac_admin_role] - 'Received a TACACS+ Accounting stop request. Terminated Session.' |
|---|
- Session deletion due to session timeout.
Info | ADM20664 | 2018-01-30 19:34:40 - ic - [xx.xxx.xx.xxx] tac_user(tac_admin_realm)[tac_admin_role] - Session timed out for tac_user/tac_admin_realm due to inactivity (last access at 19:29:38 2018/01/30). Idle session identified during routine system scan. |
|---|
- Enable Authentication: [Only when Administrator login is enabled under admin access setting]
- Enable authentication success.
Info | AUT30684 | 2018-01-30 19:28:09 - ic - [xx.xxx.xx.xxx] tac_user(tac_admin_realm)[] - Enable Service authentication successful for tac_user/System Local from 10.204.59.223(Shell login to 10.204.88.10). |
|---|
- Login failure due to authentication failure.
Info | AUT23458 | 2018-01-30 19:29:44 - ic - [xx.xxx.xx.xxx] tac_user(tac_admin_realm)[tac_admin_role] - Login failed using auth server System Local (Local Authentication). Reason: Failed |
|---|
- Login failure due to restrictions.
Info | AUT23458 | 2018-01-30 19:31:15 - ic - [xx.xxx.xx.xxx] tac_user(tac_admin_realm)[tac_admin_role] - Login failed. Reason: No Roles |
|---|
- Login failure due to no role available.
Info | AUT23458 | 2018-01-30 19:31:15 - ic - [xx.xxx.xx.xxx] tac_user(tac_admin_realm)[tac_admin_role] - Login failed. Reason: No Roles |
|---|
- Assigning custom attributes from IPS to TACACS+ client (Juniper, F5)
Info | TAC31778 | 2019-04-23 11:55:11 - IPS- [127.0.0.1] user7(Admin realm)[networkadmin] - User assigned TACACS+ attribute(s) (local-user-name=network-admin user-permissions=view deny-commands=show firewall$ allow-commands=edit*) |
|---|
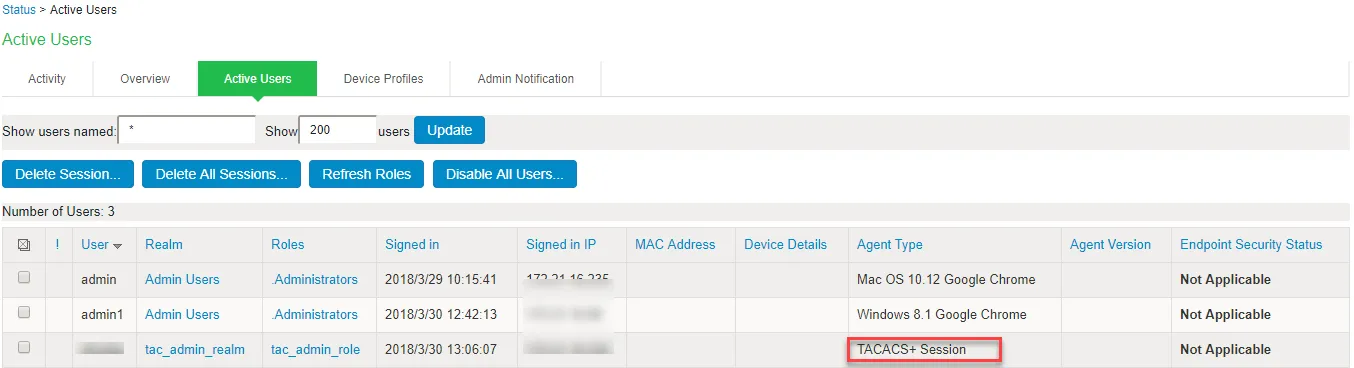
Once the session is established the session is seen as TACACS+ Session in the Active Users Page