Troubleshooting
2 min
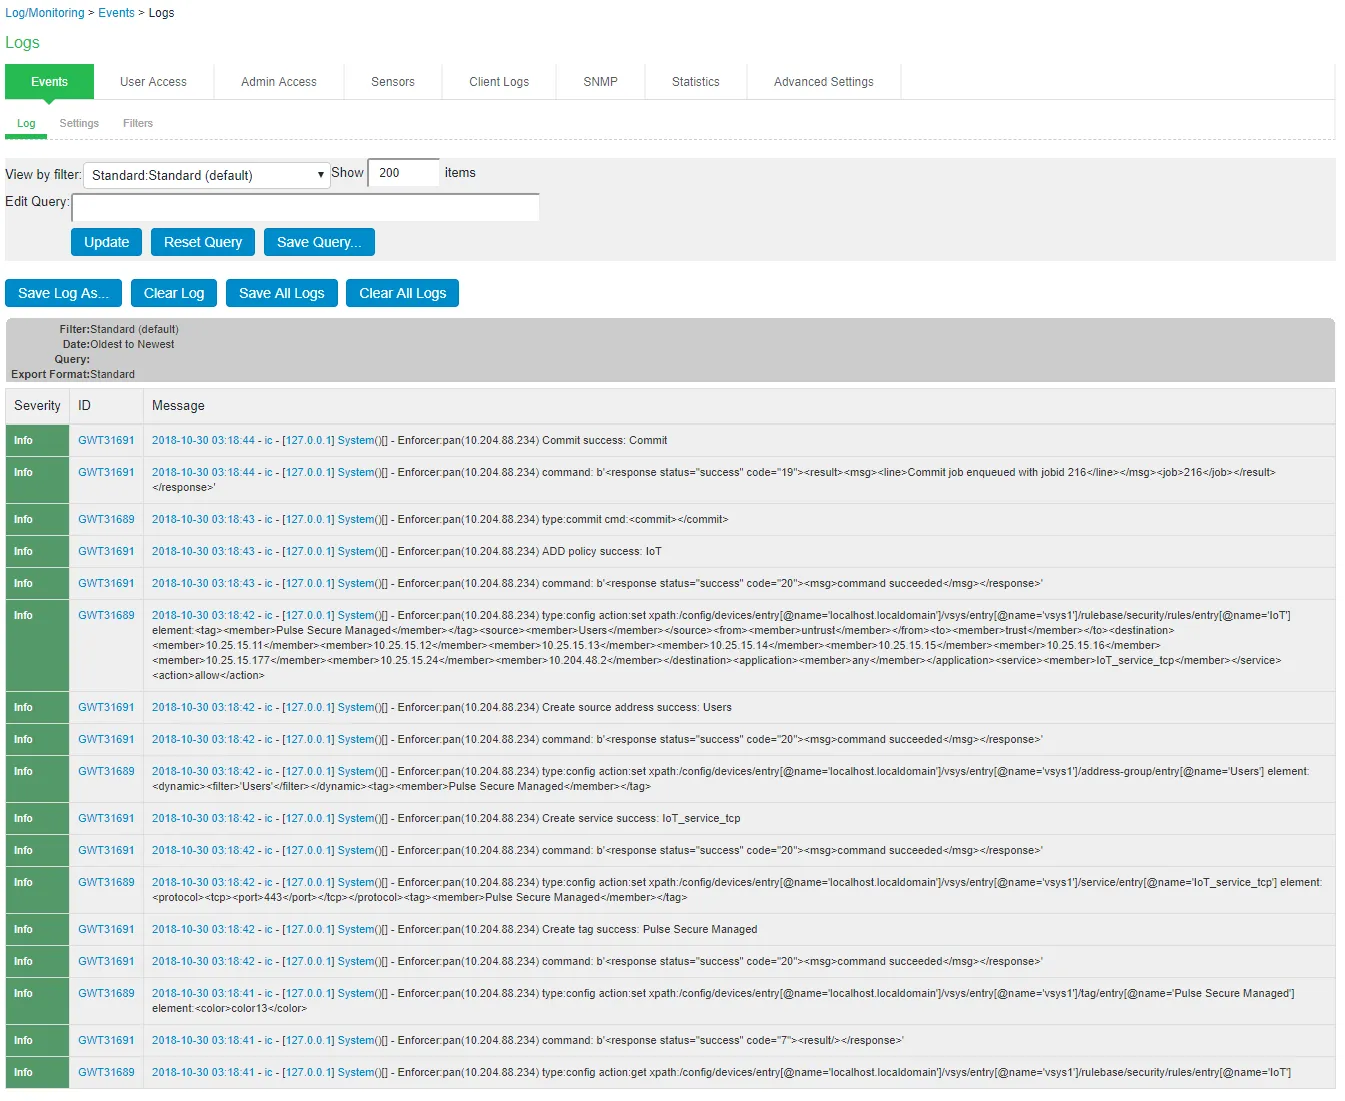
The event and debug logs can be used for troubleshooting:
- The Event logs are generated whenever the policies are pushed to firewall.
- The Admin Logs are generated upon policy provisioning and auto updation of newly discovered devices.
You can also use Maintenance > Troubleshooting > Monitoring > Debug Log for debugging issues.
If the device is not discovered properly in the IoT Policy Provisioning > Enforcer Policy Report page check the Device Discovery Report page for the device category.
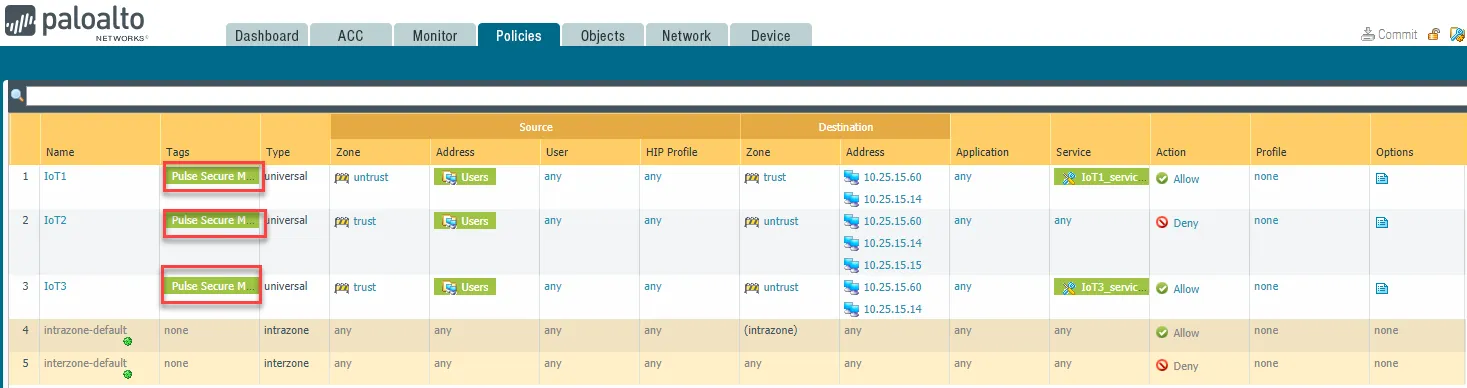
The IPS created policies on PAN firewall should not be modified by the PAN admin. The IPS created policies on Palo Alto Networks firewall are tagged as Pulse Secure Managed.
Event Logs
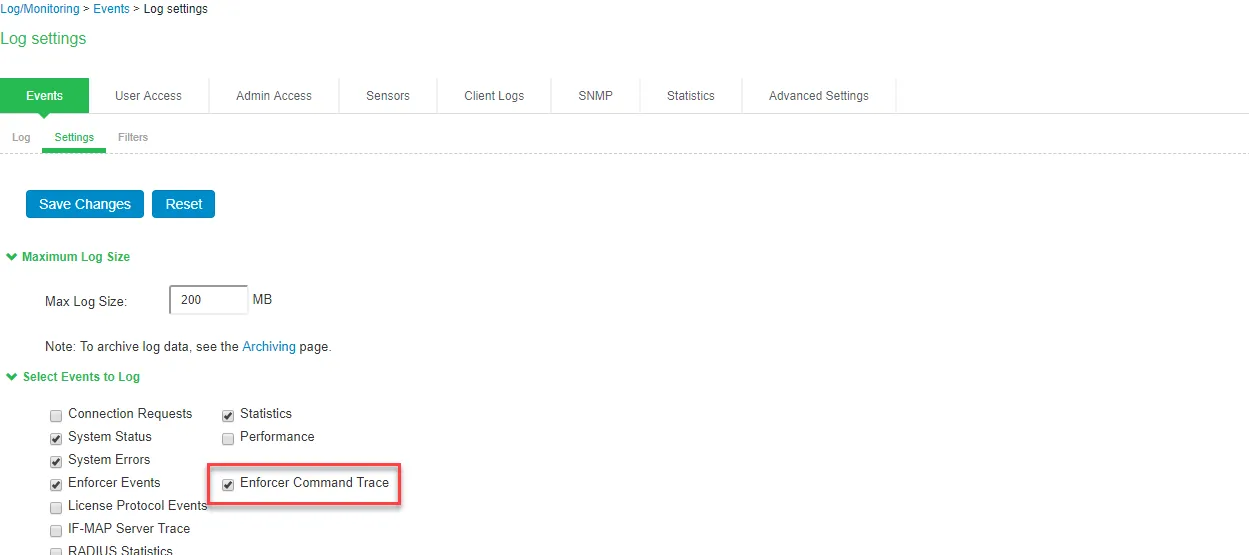
To view the communication between IPS and Infranet Enforcer enable Enforcer Command Trace under Events > Settings.
A sample event logs is shown in figure.