Configuring Firewall Provisioning based on Profile Group
To configure firewall provisioning based on Profile group:
- Admin configures local profiler on IPS to discover devices connected to network. For Profile group configuration, see Configuring Profiler Groups. Auth Table Timeout option is used for dynamic auth table policy provisioning to firewall (Applies only to SRX firewall).
- Configure firewall as an Enforcer, select Endpoint Policy > Infranet Enforcer > Connection and add the enforcer.
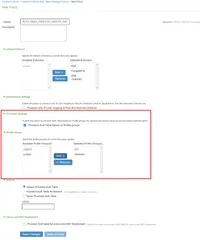
- Configure Auth Table Mapping Policy based on Profile Group, select Endpoint Policy > Infranet Enforcer > Auth Table Mapping. Under Provision Settings, enable Provision Auth Table based on Profile Groups.
- Select the Profile Group to which the policy applies and click Add and then click Save Changes.
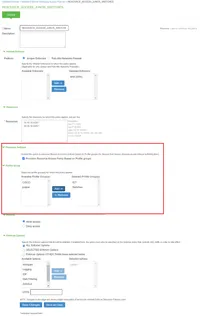
- Configure Resource Access Policy based on Profile Group, select Endpoint Policy > Infranet Enforcer > Resource Access Policy. Under Provision Settings, enable Provision Resource Access Policy based on Profile Groups.
- Select the Profile Group to which the policy applies and click Add and then click Save Changes.
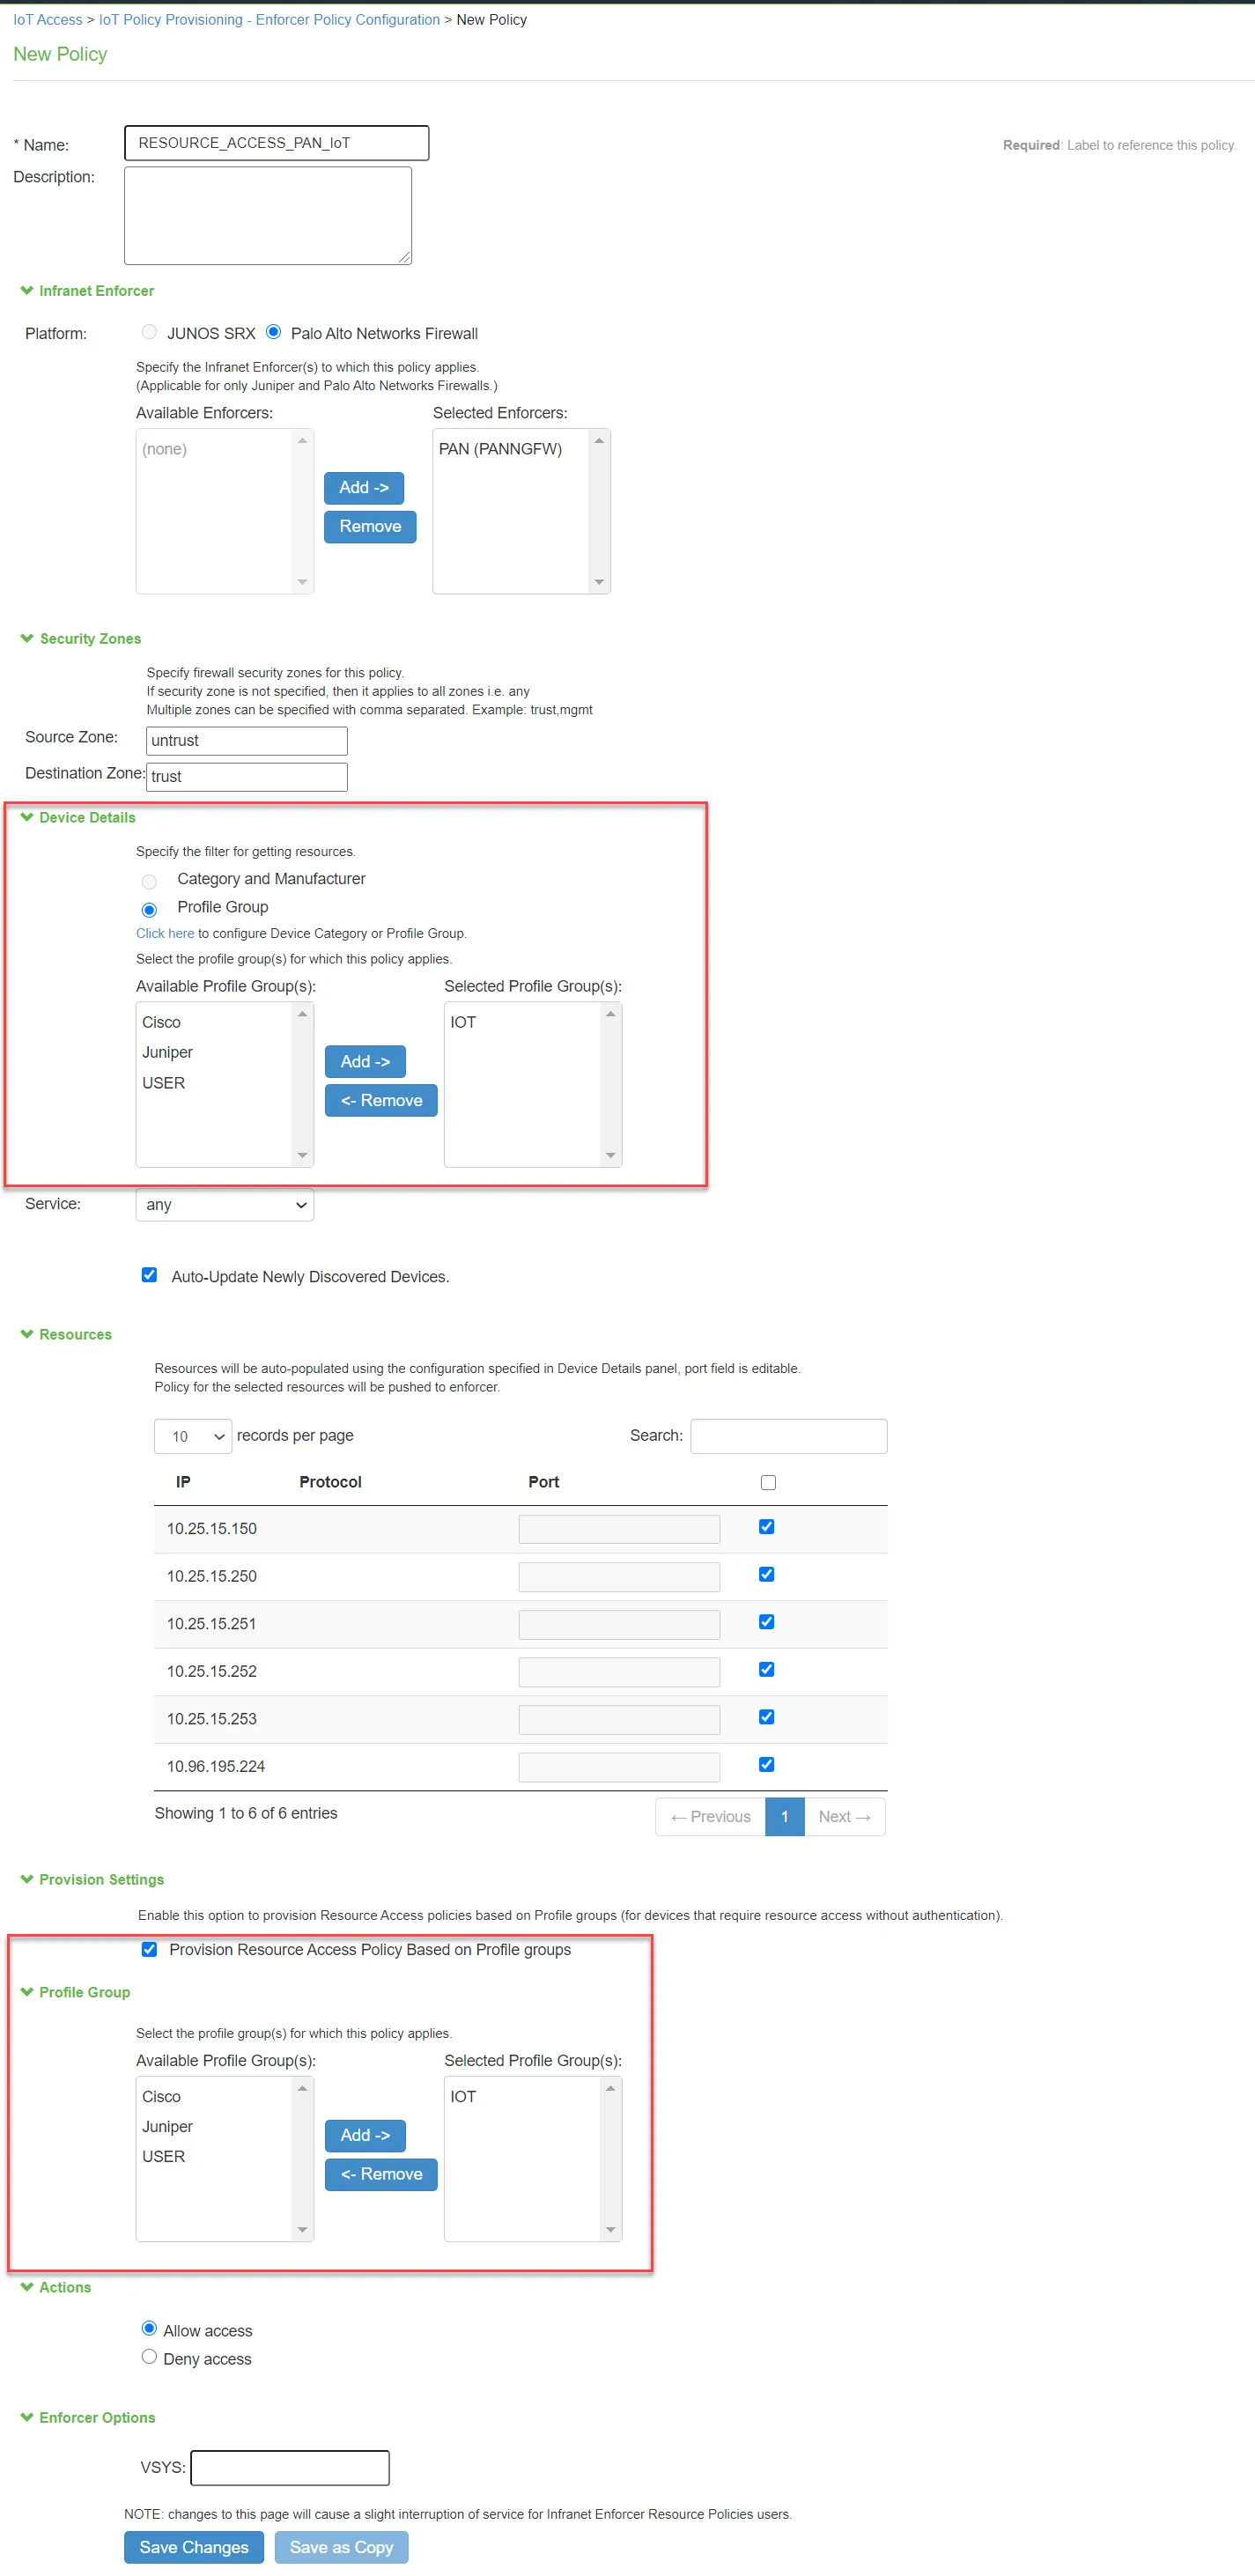
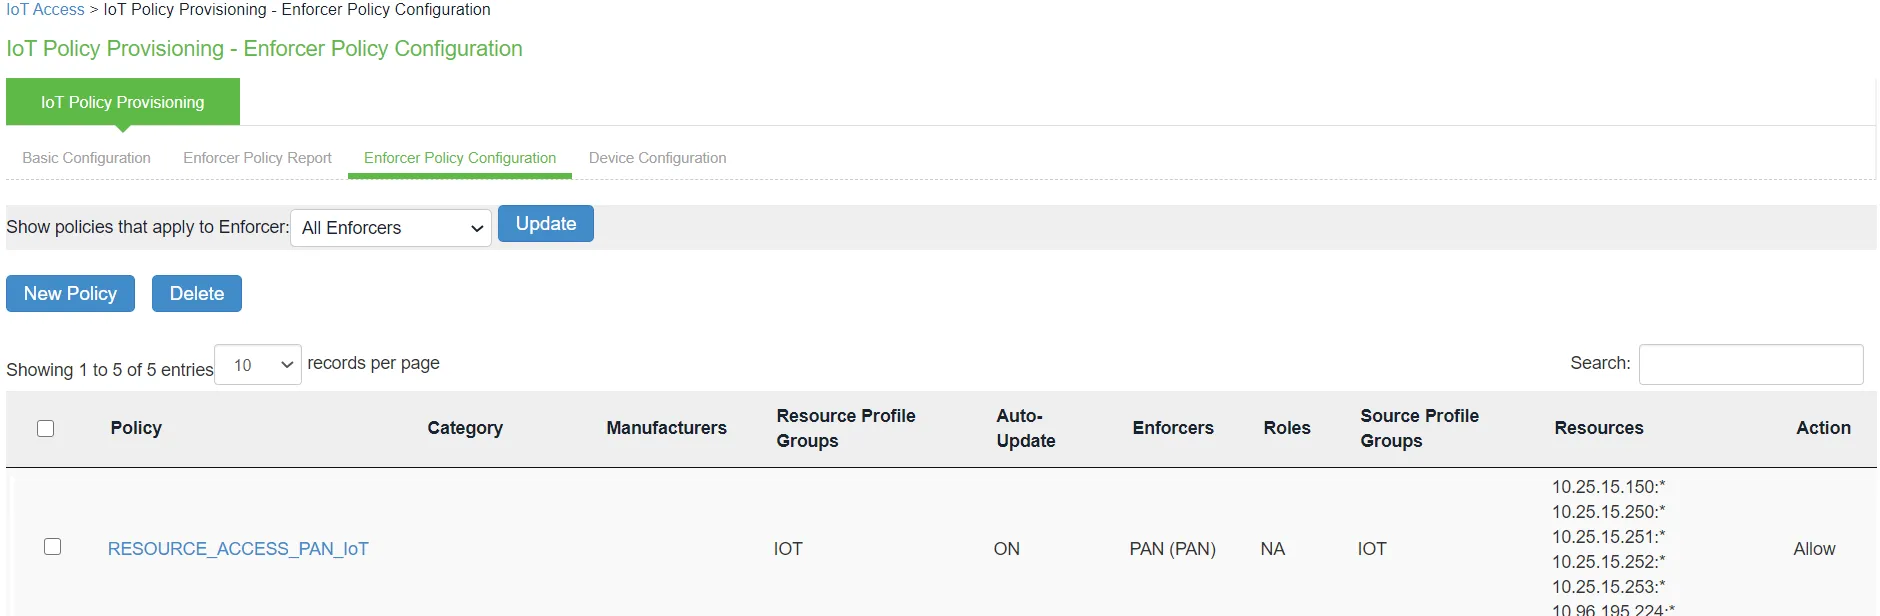
- For IoT access policy, select Endpoint Policy > IoT Access > Enforcer Policy Configuration. Under Provision Settings, enable Provision Resource Access Policy based on Profile Groups.
- If there are Auth Table Mapping Policies based on Roles as well as Profile Groups and if there is an authenticated session for an endpoint which is also profiled and belongs to group(s), then user roles will be given precedence over profiler groups for firewall provisioning. - If the user is logged out but profiled information is still available in the Profiler database then endpoint information will not be provisioned to firewall based on profile groups. However, it will be synced with firewall during next reconciliation. - If there is an authenticated session and if the Auth Table Mapping policy provisioning is changed to groups from roles then the corresponding entry may get deleted from the firewall if there are no other policies applying to the user role(s).